

Operational compliance is the continuous process of embedding legal, regulatory, and internal policy requirements directly into daily workflows so your organization can prove those controls actually run, not just exist on paper. The single most useful distinction: regulatory compliance defines which rules apply; operational compliance is how you build those rules into processes and generate the evidence that demonstrates ongoing adherence. If you do nothing else today, spend 30 minutes mapping one high-risk workflow and identifying where the control evidence currently lives.
Key Takeaways
Operational compliance is only as strong as the evidence your daily workflows produce — programs that treat policy creation as the endpoint consistently fail audits.
| Point | Details |
|---|---|
| Definition | Operational compliance embeds rules into daily workflows and generates durable evidence that controls actually run. |
| Regulatory vs. operational | Regulatory compliance identifies the rules; operational compliance proves you follow them through documented processes. |
| 30/60/90 priority | Start by mapping your three highest-risk workflows and assigning one named owner to each control within 30 days. |
| Measurement | Track task completion rate, mean time to remediate, and permit renewal on-time rate as your core executive KPIs. |
| Vaultedai | Vaultedai centralizes permits, automates renewal reminders, and provides jurisdiction-specific checklists for multi-location teams. |
Table of Contents
- What does operational compliance mean in practice?
- What are the main types of compliance requirements?
- What are the key elements of an operational compliance program?
- Why does operational compliance matter for your business?
- How to operationalize compliance: a step-by-step plan
- What tools support operational compliance programs?
- How do you measure operational compliance success?
- Common challenges in operational compliance and how to fix them
- When should you consider compliance software?
- Your 30/60/90-day operational compliance checklist
- The part most compliance programs get wrong
- Vaultedai: built for multi-location compliance teams
- Sources
What does operational compliance mean in practice?
Operational compliance is the proactive, continuous process of integrating regulatory and policy requirements into daily workflows so controls execute and produce durable evidence. That last phrase matters: durable evidence. A policy document filed in a shared drive is not operational compliance. A completed safety inspection log, a timestamped data-handling approval, or an auto-generated permit renewal reminder tied to a specific location — those are.
Day-to-day, operational compliance works through three mechanisms: controls embedded in workflows (a checklist that cannot be skipped), continuous evidence generation (logs, approvals, signed records), and regular review cycles that catch drift before it becomes a violation. Regulatory compliance, by contrast, is largely a legal determination — your attorneys identify the obligations; your operations team has to make them real.
Three quick examples show the difference clearly. A restaurant group's OSHA-required safety log, completed by a shift manager every morning, is operational compliance. A healthcare company's data-handling workflow that routes every patient record through an access-controlled system and logs each retrieval is operational compliance. A franchise chain's permit renewal calendar, with automated reminders 90 days before each expiration, is operational compliance. In each case, the rule exists because of a regulator; the daily execution is what makes the organization compliant in practice.
What are the main types of compliance requirements?
Compliance requirements fall into three practical categories, and understanding which bucket a given obligation belongs to tells you who owns it and what evidence you need.
| Category | Purpose | Primary Owner | Evidence Type |
|---|---|---|---|
| Regulatory / legal | Meet government-mandated rules (OSHA, EPA, FinCEN, FDA) | Legal / compliance officer | Inspection logs, filings, permits |
| Industry / standards | Align with sector frameworks (NIST, ISO, COSO) | IT, operations, or quality | Audit reports, certifications |
| Internal / policy | Enforce company-specific SOPs and codes of conduct | Department managers | Signed acknowledgments, training records |
For implementers, the working definition is this: an operational compliance requirement is any obligation that must be evidenced through a repeatable, documented workflow rather than a one-time declaration. That framing tells you immediately whether a requirement needs a process owner, a control, and a retention schedule — or whether it can be handled with a single legal filing and forgotten.
What are the key elements of an operational compliance program?
Seven building blocks make up a functional program. Miss one and you typically find out during an audit.
| Element | Owner | Example Artifact |
|---|---|---|
| Policies and SOPs | Compliance officer | Written procedure with version history |
| Roles and accountability | Department heads | RACI chart, signed job descriptions |
| Controls and automation | IT / operations | Workflow gate, automated approval step |
| Monitoring and logging | IT / compliance | Audit log, dashboard alert |
| Training | HR / compliance | Completion certificate, LMS record |
| Recordkeeping | Operations | Retained permit, timestamped approval |
| Incident handling | Compliance / legal | Incident report, corrective action plan |
What good looks like in each area is specific. A solid SOP includes a version date and a named approver. A RACI chart assigns one accountable person per control, not a committee. Automated controls generate a log entry every time they fire. Monitoring surfaces exceptions to a named reviewer within a defined window. Training records show completion dates, not just enrollment. Retained records carry metadata (who, when, what action). Incident reports close with a documented root cause and a corrective action deadline.
Operational compliance emphasizes proving controls work in practice through repeatable workflows, durable evidence, and reviewable decisions that survive audit scrutiny. That standard applies to all seven elements, not just the ones that feel most visible.
Why does operational compliance matter for your business?
The short answer: it keeps the business running, reduces fines, and protects the people at the top of the org chart from personal exposure.
On the benefit side, a mature operational compliance program protects revenue by reducing the likelihood of enforcement actions that trigger fines or forced shutdowns. It builds operational resilience because documented workflows survive staff turnover — a new shift manager can follow the same safety checklist the previous one used. Audit readiness improves because evidence is collected continuously rather than assembled in a panic before an inspection. Compliance also affects your insurance profile directly; carriers increasingly price coverage based on documented control environments, and a strong compliance posture can reduce premiums.
The risk side is harder to ignore. Enforcement actions can produce fines, operational interruptions, and individual executive exposure. Failure to maintain operational controls and evidence can leave organizations exposed even when policies exist on paper — regulators and plaintiffs look at what actually happened, not what the policy said should happen.
The financial cost of weak controls is concrete. The average cost of a U.S. data breach illustrates what happens when operational controls around data handling fail — and that figure covers only one category of compliance failure, not safety violations, permit lapses, or AML penalties.
Thomson Reuters' Risk and Compliance Survey found that many organizations still struggle with evidence collection and monitoring — exactly the gaps a well-designed operational compliance program closes.
How to operationalize compliance: a step-by-step plan
The single highest-priority action is to map the workflows tied to your highest regulatory or operational risk first. Everything else follows from that map.
-
Inventory your obligations. List every regulatory, standards, and internal requirement that applies to your business. Group by category (safety, data, permits, financial reporting). 30-day milestone: complete obligation inventory with assigned category and risk tier.
-
Map critical workflows. For each high-risk obligation, trace the current workflow from trigger to evidence. Identify gaps where no control exists or where evidence is not retained. 30-day milestone: at least three high-risk workflows documented.
-
Assign owners. Every control needs one accountable person, not a team. Use a RACI chart. 30-day milestone: RACI complete for all high-risk controls.
-
Instrument controls. Replace manual steps with automated ones where possible. Permit renewal reminders, access-controlled data workflows, and automated safety checklists all reduce human error and generate logs automatically. 60-day milestone: at least two manual controls converted to automated or semi-automated.
-
Monitor and report. Set up a dashboard that surfaces exceptions. Define who reviews it and how often. 60-day milestone: first internal evidence audit completed; exceptions documented.
-
Baseline KPIs and present to leadership. Run your first formal KPI report. Show task completion rates, open findings, and mean time to remediate. 90-day milestone: dashboard presented to leadership with corrective action plan for any open items.
Pro Tip: Start with recurring permit renewals. They have fixed deadlines, clear evidence requirements, and the cost of missing one is immediate and measurable. A single missed permit can trigger a shutdown — making it the fastest place to demonstrate the value of an operational compliance program.
Pro Tip: High-risk data flows are your second quick win. Map where personal or regulated data enters, moves, and exits your systems. EPA regulations and FinCEN's AML requirements both impose ongoing operational obligations — logging, reporting, and recordkeeping — that are easy to automate once the flow is mapped.
For teams scaling across locations, the business scaling compliance strategy layer adds complexity: each new location may add jurisdiction-specific obligations, so the inventory step needs to repeat for every new market.
What tools support operational compliance programs?
Tool categories map roughly to the seven program elements. No single platform covers everything, but the right stack reduces manual work and closes evidence gaps.
Compliance management platforms centralize obligation tracking, document storage, and renewal calendars. Look for jurisdiction-specific checklists, automated reminders, and audit logs built in. For multi-location operators, multi-entity support and bulk actions are non-negotiable.
Workflow automation tools convert manual approval steps into logged, auditable processes. The key feature is an immutable audit trail — every action timestamped and attributed to a named user.
Logging and monitoring systems surface exceptions in real time. Integration with your compliance platform via API means evidence flows automatically rather than requiring manual export.
Identity and access management (IAM) tools enforce role-based access to sensitive data and generate the access logs regulators expect. SSO integration reduces friction for end users while maintaining control.
Document and evidence repositories retain records with metadata intact. Version control, retention schedules, and search are the three features that matter most when an auditor asks for a document from 18 months ago.
Selection checklist for any platform: audit logging built in, configurable evidence retention, jurisdiction-specific checklists, automated renewal reminders, role-based access, mobile workflows, and API access for integration. For multi-location teams, add bulk actions and multi-entity dashboards to that list. A useful starting point for comparing platforms is this compliance management software overview, which covers feature trade-offs across current options.
How do you measure operational compliance success?
Track four dimensions: process completion, control effectiveness, evidence availability, and time to remediation. Everything else is a derivative of those four.
| KPI | Definition | Sample Target |
|---|---|---|
| Task completion rate | % of required compliance tasks completed on time | 95% or above |
| Audit findings per period | Number of control gaps identified per audit cycle | Trending down quarter over quarter |
| Mean time to remediate (MTTR) | Average days from finding identification to closure | Under 30 days |
| Evidence coverage ratio | % of controls with complete, retrievable evidence | 90% or above |
| Permit renewal on-time rate | % of permits renewed before expiration | 100% |
For executive dashboards, surface task completion rate, MTTR, and permit renewal rate. Those three tell a leadership team whether the program is functioning without requiring them to understand the underlying controls. Operations leads need the full table plus exception detail — which specific controls are failing and who owns the remediation.
NIST, ISO, and COSO frameworks provide control design guidance that maps well to these KPIs. NIST CSF, for example, structures controls around identify, protect, detect, respond, and recover — each of which has a measurable analog in the KPI table above.
Common challenges in operational compliance and how to fix them
Most programs fail in predictable ways. The fixes are equally predictable, which means there is no excuse for repeating them.
- Lack of ownership. Controls assigned to "the team" get done by no one. Fix: assign one named accountable person per control in a RACI chart. Review it quarterly.
- Evidence gaps. Policies exist; proof of execution does not. Fix: automate evidence capture at the control level — a completed checklist that generates a timestamped log, not a verbal confirmation.
- Tool sprawl. Compliance data lives in five systems that do not talk to each other. Fix: consolidate to a single compliance platform or build API integrations so evidence flows to one repository.
- Manual renewals. Permit and license deadlines tracked in a spreadsheet get missed when the person who owns the spreadsheet leaves. Fix: centralize renewals in a system with automated reminders tied to the deadline, not to a person.
- Cross-jurisdiction confusion. A multi-location operator discovers that what is required in Texas differs from California, and no one mapped the differences. Fix: build a jurisdiction-specific obligation inventory for each location before opening, not after.
A recurring failure pattern: a regional manager at a multi-location food service operator tracks health permits in a personal spreadsheet. When that manager transfers, the spreadsheet goes with them. Three months later, two locations are operating on expired permits. The fix is not a better spreadsheet — it is a centralized system where the permit record belongs to the location, not the person. Growing businesses that move from spreadsheets to compliance tools consistently cite this exact scenario as the trigger.
When should you consider compliance software?
Move from spreadsheets to a compliance platform when any of these conditions apply: you manage recurring renewals across more than two locations, you receive frequent evidence requests from auditors or regulators, or you have missed a deadline in the past 12 months. Those three triggers indicate that the manual system has already exceeded its capacity.
Feature priorities for multi-location operators:
- Centralized document repository with metadata and version control
- Automated renewal reminders with configurable lead times
- Jurisdiction-specific compliance checklists
- Immutable audit logs
- Mobile access for field teams
- Role-based access control
- Multi-entity support and bulk actions
For teams evaluating options, why businesses use compliance software covers the operational triggers and feature trade-offs in detail. If you want implementation support alongside a platform, AITHEA offers AI-enabled compliance and risk consulting for organizations that need both tooling and advisory guidance.
Vaultedai is one option purpose-built for this use case: multi-location businesses that need centralized permit tracking, automated reminders, and jurisdiction-specific checklists without building a custom system.
Your 30/60/90-day operational compliance checklist
30-day priorities
- Inventory all regulatory, standards, and internal obligations by location. Success indicator: complete list with risk tier and category.
- Identify the three highest-risk controls and map their current workflows. Success indicator: workflow diagram with evidence gaps marked.
- Assign one named owner to each high-risk control. Success indicator: RACI chart signed off by department heads.
- Capture quick wins: set up renewal reminders for any permits expiring in the next 90 days. Success indicator: zero permits expiring without a reminder in place.
60-day priorities
- Automate at least two recurring manual controls (safety checklists, data access approvals). Success indicator: automated workflow generating a log entry per execution.
- Run your first internal evidence audit against the three mapped workflows. Success indicator: evidence coverage ratio calculated for each.
- Document and assign corrective actions for every gap found. Success indicator: each gap has an owner and a due date.
90-day priorities
- Baseline all five KPIs from the measurement section. Success indicator: first KPI report produced.
- Present the dashboard to leadership with open findings and remediation status. Success indicator: leadership sign-off on corrective action plan.
- Review the obligation inventory for any new locations or regulatory changes. Success indicator: inventory updated and re-tiered.
The part most compliance programs get wrong
Operational compliance programs tend to fail not because organizations lack policies, but because they treat policy creation as the finish line. The real work starts after the policy is written: instrumenting the control, assigning a real owner, and collecting evidence that would hold up if an auditor walked in tomorrow.
The trade-off most teams face is between coverage and depth. You cannot instrument every control on day one. The right call is to go deep on the three or four workflows that carry the most regulatory or financial risk, get those producing clean evidence, and then expand. A program with three well-evidenced controls is more defensible than one with thirty controls that exist only on paper.
Start with one workflow this week. Map it, assign an owner, and identify where the evidence currently lives. That single exercise will surface more actionable information than a month of policy drafting.
Vaultedai: built for multi-location compliance teams
Multi-location operators managing permits, licenses, and renewals across dozens of sites face a specific problem: the compliance burden scales with every new location, but the team rarely does. Vaultedai is built for exactly that gap.
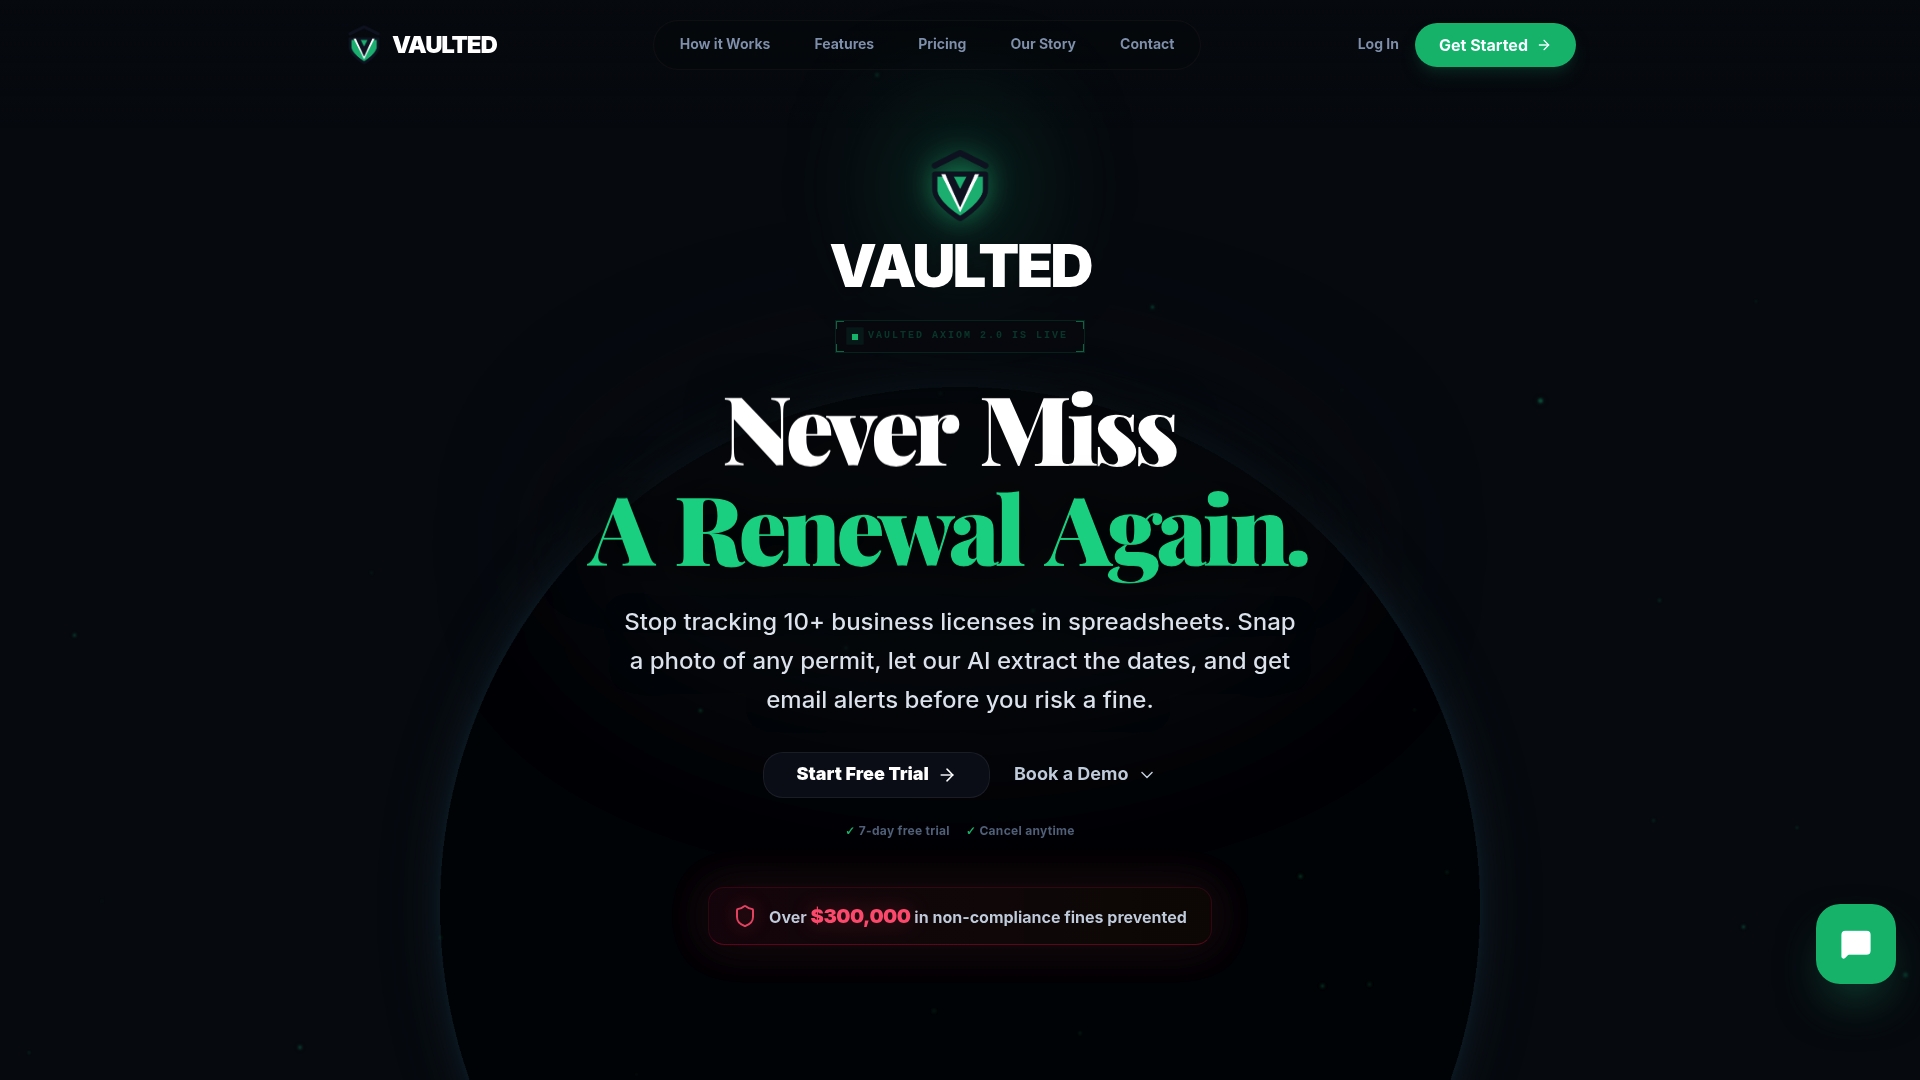
The platform centralizes permits, licenses, renewals, and compliance documents across all locations in one place. Automated renewal reminders fire before deadlines, not after. Jurisdiction-specific checklists mean your team knows what is required in each market without building the list from scratch. AI-powered document data extraction pulls key dates and details from uploaded permits automatically, and secure cloud and mobile access keeps field teams connected to the same records as the compliance office. If your team is ready to move off spreadsheets, start with Vaultedai and see how fast onboarding works in practice.
Sources
- Average cost incurred by a data breach in the U.S. | Statista